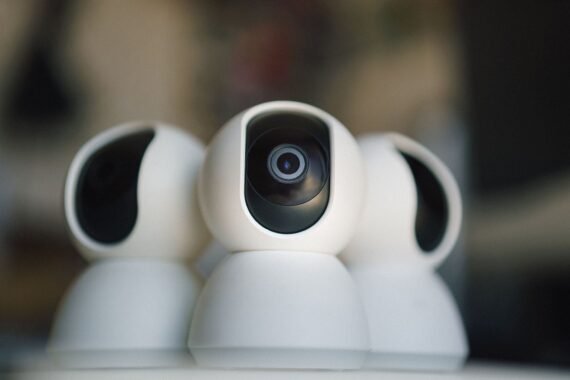
Among the cheap IP cameras commonly used in homes and shops, Yoosee-branded models have been found to send live video over the network without encryption. The vulnerability, recorded as CVE-2026-116116, affects Yoosee cameras with the GM8135S chip and firmware up to version 21.00.01.36. Researcher Brylle explained their findings step by step in their own writeup.
Live video flows in cleartext on the network
The camera’s /npc/npc binary does not encrypt the video stream it sends over UDP during live viewing. An attacker positioned on the network can capture packets while the stream is active and reconstruct the image. Because no transport layer security (TLS) is used, this means anyone on the same network or along the traffic path can join the viewing window. NVD classified this behavior as cleartext transmission of sensitive information.
The camera connects to open networks on its own
The second point highlighted by the researcher is that the device is configured to automatically connect to unencrypted default Wi-Fi networks. When the camera finds one of these networks nearby, it connects without asking the user, making it easier for someone who wants to eavesdrop. This situation, caused by the device’s default configuration, makes the camera more exposed without the person who set it up realizing it.
Firmware is not verified
The firmware stored in the camera’s SPI flash memory (XM25QH64) does not undergo signature verification when the device boots. As a result, the software can be read, modified, and written back. NVD recorded this part as lack of cryptographic signature verification and rated the vulnerability 8.4 on the CVSS 4.0 scale and 8.2 on the CVSS 3.1 scale. This step, which requires physical access, means someone with access to the camera can permanently modify the device’s software.
No response from the manufacturer
The researcher says they reported the findings to the manufacturer, but received no response. The exploit code is publicly available, and there is no published patch at the moment. Yoosee cameras are also sold at low prices on online marketplaces in Turkey; the model’s prevalence means the risk is not limited to a single user.
What to do
- Isolate the camera from the main network; run it on a guest network or a separate VLAN.
- Check the camera’s saved Wi-Fi networks and delete unknown open networks.
- Remove port forwarding rules for the camera on the modem and disable external access.
- If possible, switch to a camera that offers encrypted streaming and signature verification.
The lack of encryption for camera footage is not a problem that can be fixed by measures on the recorder or cloud side. Network-side isolation stands out as the only effective measure available.
Share your experience
Bir sorunun, farklı bir çözümün veya eklemek istediğin bir notun var mı? Giriş yapmadan da yazabilirsin.