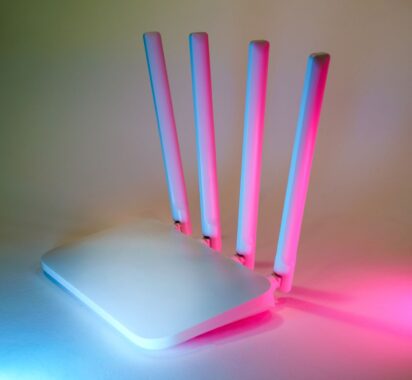
A router that’s been running at home for years is the quietest yet most critical part of your network. The disclosures published this week for two older models target exactly these devices: the D-Link DIR-600L and the TRENDnet TEW-657BRM. Both issues were rated 10.0 on the CVSS scale, and exploit code is publicly available.
The login screen on the D-Link DIR-600L is vulnerable
The B hardware revision of the D-Link DIR-600L running firmware 2.17b02 does not perform bounds checking in the login handler in the authentication.cgi file. The username and password fields are copied without limits into fixed-size buffers; a long login attempt corrupts adjacent memory. In the analysis published by the researchers, an unauthenticated request causes the CGI process to crash, and the faulting address shifts to a value chosen by the attacker.
There is also a second vulnerability in the same model: the HNAP handler writes the action name it takes from the HTTP SOAPAction header into a 256-byte buffer without limits. Because the whitelist check is evaluated separately from the suffix added by the attacker, this path can also be reached without authentication. The two issues are tracked as CVE-2026-129353 and CVE-2026-129354.
The redirect address overflows on the TRENDnet TEW-657BRM
On the TRENDnet TEW-657BRM (firmware 1.00.1), the problem is inside the mini_httpd server. When a request path containing .htm arrives, the server builds a redirect address in a fixed-size global buffer and does not enforce a length limit. The write happens before HTTP Basic authentication. The researchers report that they gained control of the program counter in firmware running under QEMU and executed a harmless test payload. This issue is tracked as CVE-2026-129351.
So how serious is this?
Neither vendor is confirming the vulnerabilities. TRENDnet says the product has been unsupported for more than 15 years and states that it will not release a patch. There is no fix from D-Link either. The research notes clearly say that most of the evidence was gathered in an emulator and that code execution on a physical device has not been confirmed. So the 10.0 score reflects the theoretical impact of the flaw; it does not mean there is a fully confirmed attack chain.
Still, don’t underestimate it. Exploit code is public, the devices are still out there, and the management interface can even end up exposed to the internet when misconfigured. Vulnerabilities like these are often used as an entry point for botnets.
What should you do?
If you use either of these two models, the first option is to replace the device. An unsupported router does not become safe by waiting for a patch. If you can’t retire it immediately, a few steps can reduce the risk:
- Block access to the management interface from the WAN side, and disable remote management.
- Make the management interface accessible only from a local network you trust.
- Do not leave the router on the same network as the modem; use a separate segment such as a guest network.
- If the device shows unexpected reboots, slowdowns, or traffic you do not recognize, remove it from the network.
These measures do not fix the vulnerability; they only reduce the attack surface. If one of these models is on your home network, the best move is to make a replacement plan now.
Share your experience
Bir sorunun, farklı bir çözümün veya eklemek istediğin bir notun var mı? Giriş yapmadan da yazabilirsin.