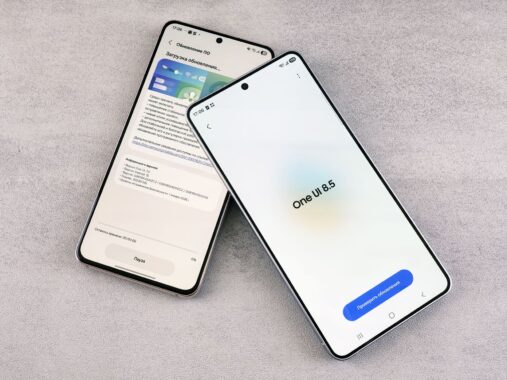
Samsung has released the October 2026 security update for Galaxy devices. The package, called SMR Oct-2026 Release 1, contains a total of 76 fixes according to Samsung’s own bulletin: 45 vulnerabilities from the Android security bulletin, 9 of them critical, 4 chipset vulnerabilities, and 27 SVE entries belonging to Samsung. The package was first rolled out to the Galaxy S26 FE; it is now rolling out to more markets, including India, Europe, and Turkey.
The highest-risk vulnerability is in the WSM service
Among the entries Samsung classifies as high, the most notable is CVE-2026-21120. The use-after-free flaw in the WSM service can lead to a local attacker executing code with system privileges. NVD gives this vulnerability a CVSS score of 8.9 and states that the entry affects Android versions 14, 15, 16, and 17.
Memory bugs in media decoders
A significant portion of the vulnerabilities is concentrated in components that process media files. The out-of-bounds write flaw in the libsmkvextractor.so library (CVE-2026-21114) and a similar flaw in libsamsungtts.so (CVE-2026-21122) allow a local attacker to execute code. In the libsimba.heifdec.media.samsung.so component, which decodes HEIF images, two separate input validation vulnerabilities (CVE-2026-21124 and CVE-2026-21125) are being fixed. Samsung states that the patches add input validation to the relevant components and that the issues were reported privately.
There are also fixes on the system side. The access control vulnerability in CocktailBarService (CVE-2026-21117), the flaw that makes it possible to access files in scoped storage through DownloadProvider (CVE-2026-21118), and the permission management issue in Locksettings (CVE-2026-21123) are closed with this package.
Chipset, Android, and app patches
The package fixes four high-risk vulnerabilities originating from Samsung Semiconductor (CVE-2026-35494, CVE-2026-68993, CVE-2026-69043, and CVE-2026-69044) along with the 9 critical entries in the Android security bulletin (including CVE-2026-20519 and CVE-2026-20520). According to the entries Samsung published, this month’s vulnerabilities are also addressed with Samsung Internet 30.0.5.24, Samsung Flow 4.9.22.4, and Samsung Checkout 5.1.03.1 versions. The company notes that some SVE entries were closed in previous updates and therefore are not separately included in the package.
How to install the update
Galaxy owners can get the update through Settings > Software update > Download and install. After installation, SMR Oct-2026 Release 1 should appear in the Security software version field under Settings > About phone > Software information; Samsung says devices that install this version receive all Samsung and Google patches in the package. Because the rollout proceeds gradually by region and model, the update may not arrive on every device the same day.
For those who regularly update their phone, this month’s package is important, especially because of the memory bugs that can be triggered through media files.
Source: Samsung Mobile Security · NVD


Share your experience
Got a question, a different solution or a note to add?
Log in or join us to write a comment.
Log in ↗︎Sign up ↗︎